The regulatory notice arrived on September 3. A reporting threshold would change on November 1 in one of Meridian Payments' markets. The document was twenty-six pages long, included an ambiguous transitional clause, and affected fraud operations, customer reporting, software rules, training, and audit evidence.
At Meridian's scale—350 employees across several regulated markets—the dangerous part was not missing the email. It was allowing different teams and AI tools to interpret the email independently.
A compliance analyst connected the publication to the regional Project in onemind. It entered as a dated legal source, not an active rule. The regulatory research assistant received the jurisdiction, current policy, source hierarchy, citation requirements, and a strict instruction to produce questions and proposals only. It identified three affected policy entries and highlighted the transitional clause for counsel.
Compliance and Legal spent four days resolving the interpretation. Their approved decision had a November 1 effective time in the market's local time zone. onemind created a future-effective entry. Live fraud tools continued using the current threshold, while the dependency engine mapped everything that would need to change: an engineering validation rule, two fraud case workflows, a training module, three reports, a support explanation, and fourteen local tool packages.
Each domain owner received a different task. Engineering approved code and tests. Fraud Operations approved the revised case steps. Training approved the training material. Support approved customer-safe language that excluded restricted fraud indicators. No single approval activated the whole change.
By October 20, onemind had built future packages in a staging state. The engineering adapter generated test configuration for Codex and the CI agent. The fraud assistant received the new decision path and escalation rules in a non-production environment. The GRC connector assembled the expected evidence chain. Validation found that one regional report still rounded the threshold using the old currency rule. The package remained not ready until the owner corrected it.
On October 30, readiness reporting showed twelve local installations current for the upcoming version, one pending, and one unreachable laptop assigned to a fraud manager on leave. The pending user had disabled automatic configuration. onemind asked for local approval rather than forcing a change. The unreachable installation became a named exception with an owner and resolution plan; it did not disappear into an aggregate percentage.
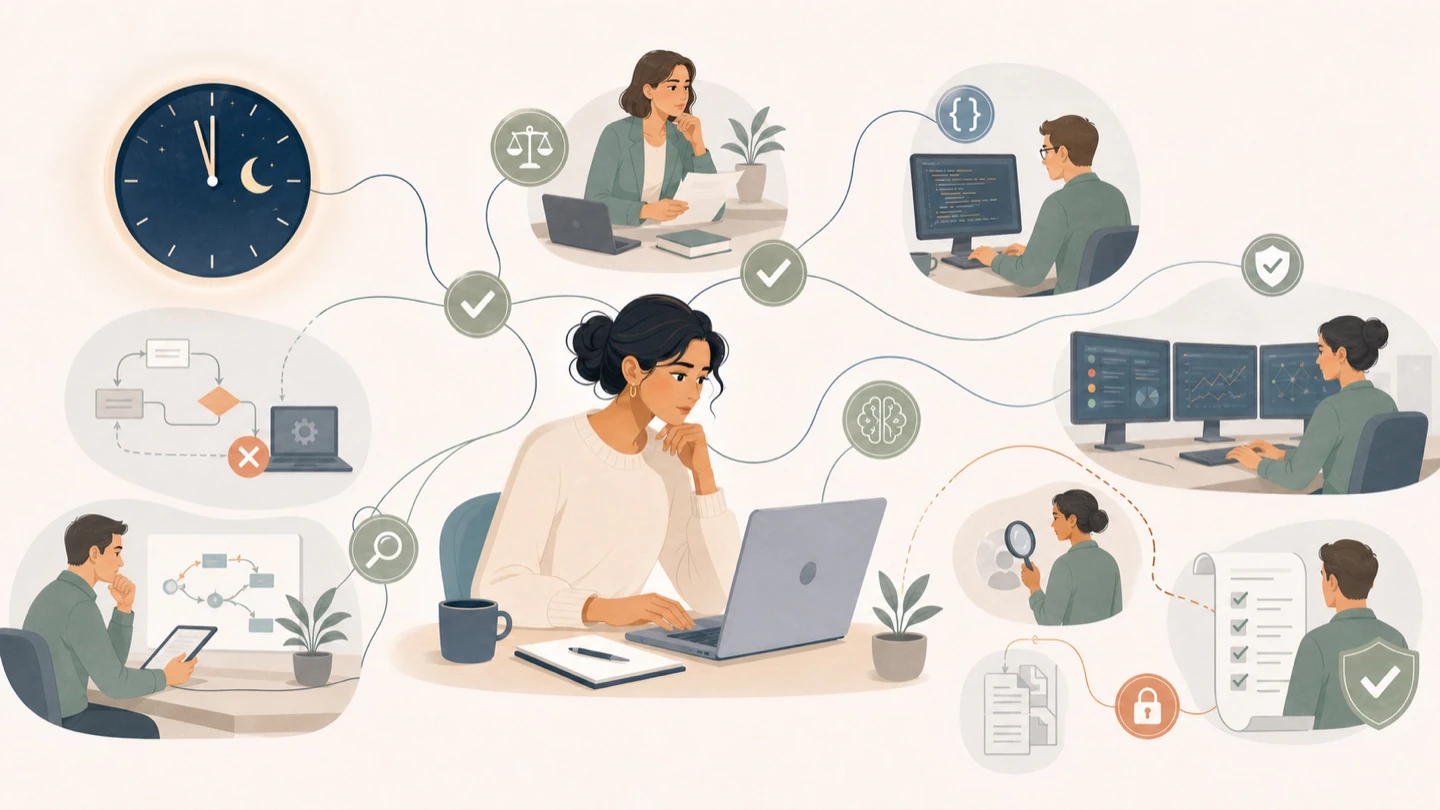
At midnight on November 1, server-side workflows activated the new package atomically. The fraud manager's unreachable laptop remained prohibited from starting the restricted reporting workflow. When the manager returned and opened it, a hook blocked the old flow, explained the required version, and offered the approved managed environment as an immediate alternative. Her general writing assistant continued to work because the restriction applied only to the fraud Project.
At 9:10 a.m., an operations lead discovered that a rare legacy case could not pass the new workflow. She requested break-glass access. onemind required a named approver, reason, affected cases, two-hour duration, and enhanced logging. Compliance approved it. The exception expired automatically at 11:30 and entered post-event review. The team later added a supported legacy path and a regression test.
During the next audit, the reviewer selected the threshold control. onemind produced the chain from regulatory publication to legal interpretation, approvals, derived entries, staged packages, validation results, local installation states, activation, the break-glass event, and the follow-up fix. What previously took several staff-days of screenshots and email reconstruction took a few hours of review and explanation.
Meridian still paid a high price to operate the system. Mapping authority, validating adapters, designing retention, and connecting the first policies had taken months. onemind could prove which approved interpretation each tool used; it could not prove the lawyers' interpretation was correct. The company's accountable people remained accountable. The gain was that their decision became one controlled operational change instead of fourteen slightly different instructions spreading through the organization.